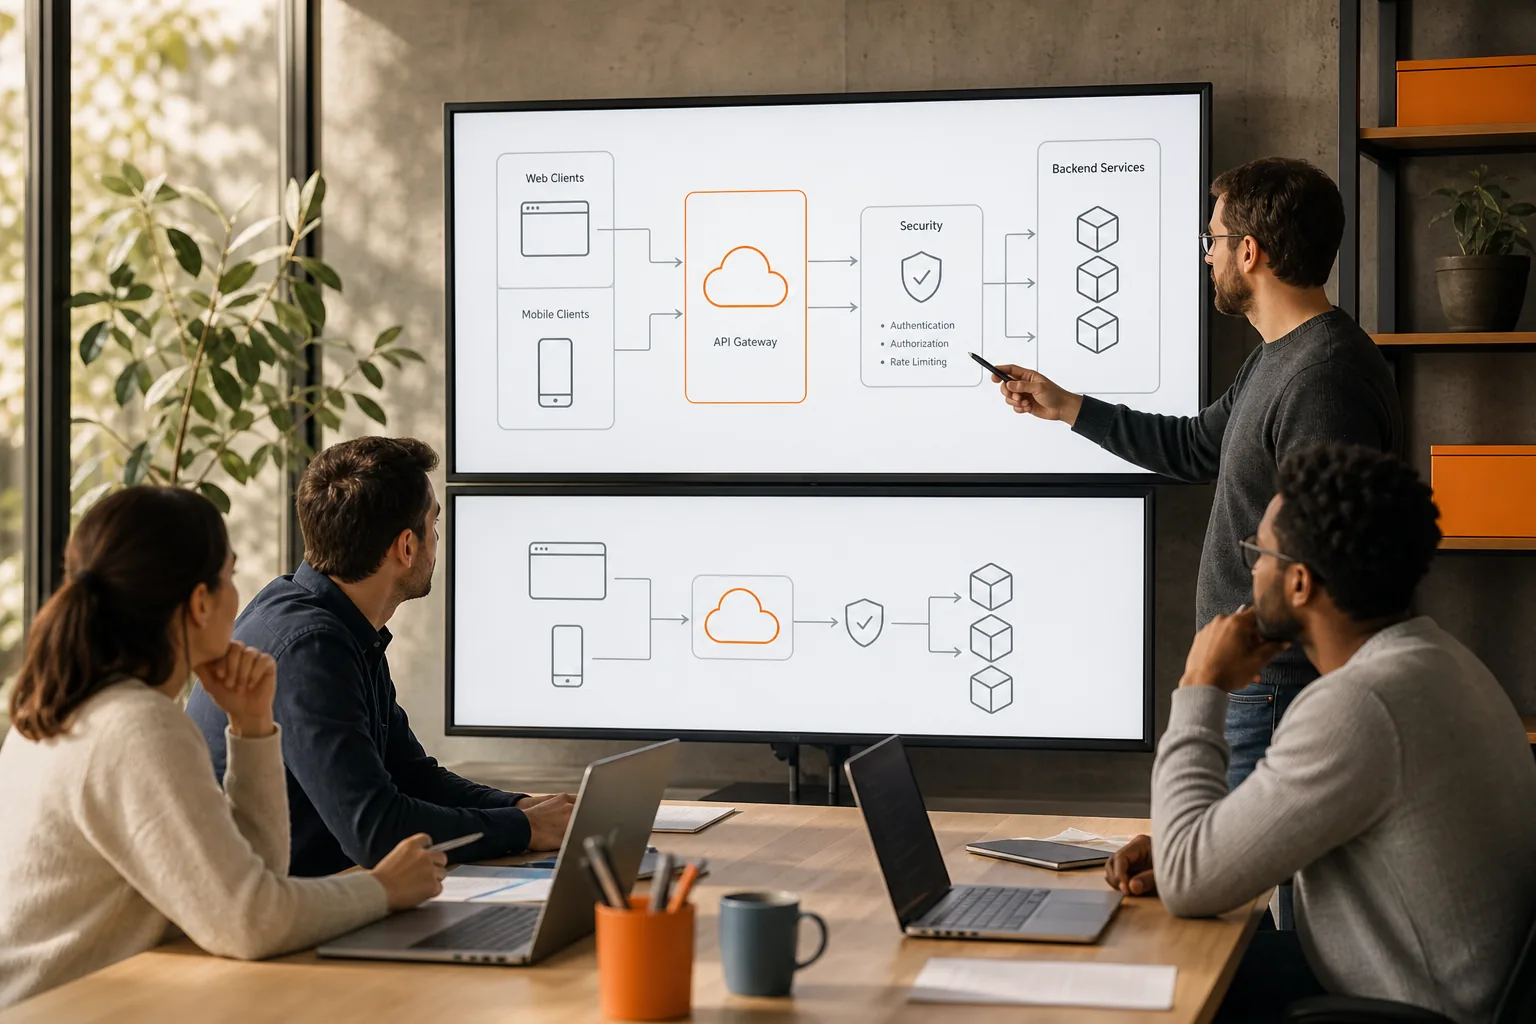
An API gateway is the front door between your clients and backend services. It routes requests, checks identity, limits abuse, and can translate protocols before traffic reaches your app. The hard part is choosing the right setup. Managed gateways are easier to run, while open-source options give you more control and may reduce license cost.
We’ll show you how to assess api gateway services, set up the main policies, and plan for growth. Lakeway Web Development can also help you connect the gateway to custom web and mobile applications.
1. Lakeway Web Development
Lakeway Web Development is the right starting point when you need a gateway plan tied to a larger application build.
An API gateway only works well when its routes match the way your app works. A web shop may need separate paths for products, orders, payments, and customer accounts. A medical practice may need stricter access rules for patient-facing features. A law firm may need clear separation between public case pages and private client data.
We design custom, responsive web and mobile applications with scalable architecture. That includes the system behind the screen, not only the page a visitor sees. Our team can map each client request to the right service, then add built-in security and clear rules for future changes.
That matters when one business has several client types. A browser, a mobile app, and a partner system may all need different responses. A gateway can present each client with a clean interface while keeping internal services private.
For mobile projects, gateway planning should happen before the app is released. The gateway becomes the shared entry point for login, data calls, file access, and account actions. Our mobile app development services can include that connection as part of the wider application plan.
We also look at the systems the gateway must connect. That may include a customer database, an accounting tool, a booking system, or an AI-powered search layer. The goal is an elegant design that fits your operations instead of adding a separate layer no one understands.
By now, you should have a short map of your clients, public routes, private routes, backend services, and data that needs protection.
Step 2: Choose a Managed, Self-Hosted, or Hybrid API Gateway
Compare api gateway services by asking who will run the gateway, where it must live, and how much control your team needs.
A managed gateway runs in a cloud provider’s environment. The provider handles much of the underlying capacity and maintenance. This can suit a small team that wants to focus on application work rather than gateway operations.
A self-hosted gateway runs inside your own container or cluster. You control its deployment and configuration. That can help when traffic must stay close to private systems, or when your team already operates Kubernetes.
A hybrid approach places some gateway functions in the cloud and others near private services. A self-hosted gateway can run as a container and be deployed to Kubernetes, AKS, or Azure Arc for hybrid and multicloud use cases. Managed options include a built-in gateway and a managed workspace gateway, while a premium offering can distribute capacity across regions. These distinctions can help you compare deployment options.
| Gateway model | Best fit | Main trade-off | First question to ask |
|---|---|---|---|
| Managed cloud | Small platform team or fast launch | Less control over runtime details | Does the service support your routes and auth needs? |
| Self-hosted | Private systems or strict deployment control | Your team owns upgrades and uptime | Who will patch and monitor each gateway instance? |
| Hybrid | Cloud plus on-premises services | More moving parts and policy work | Can one control model cover every location? |
Open-source choices can reduce license cost, but free software does not mean free operations. The documented authentication list for Apache APISIX is narrower than the “all available” authentication and authorization options described for Azure’s managed gateways. That is a useful warning: cost and capability do not always move together.
Apache APISIX supports an etcd-backed dynamic configuration mode and a standalone declarative mode. Kong supports PostgreSQL-backed, DB-less, and hybrid control-plane and data-plane modes. Envoy fits teams that mainly need a service mesh data plane, while Traefik fits teams that value provider discovery and ACME certificate automation.
Amazon API Gateway is a fully managed cloud option that supports REST and WebSocket APIs and integrates with AWS services. Azure API Management supports routing, security, throttling, caching, and observability. These services can shorten setup time, but you still need to review usage limits, support terms, data location, and expected traffic cost.
Make a written decision. Do not pick a gateway because its feature page is long. Pick the model your team can operate during a bad release or a traffic spike.
Step 3: Configure Routing, Security, and Traffic Policies
Good api gateway services act as a single entry point while keeping routing and security rules in one place.
Start with a route map. Match the public path and HTTP method to an internal service. For example,/ordersmight reach the order service, while/catalogreaches the product service. Keep internal host names out of the client-facing contract.
Path matching is only the first check. Validate the request shape before sending it downstream. Reject missing fields, invalid methods, and unexpected content types at the edge. This saves backend capacity and gives the client a clear error.
Next, set the identity flow. The gateway can check a token with an identity provider, then enforce the permissions attached to that token. Authentication answers “who is this?” Authorization answers “what may this caller do?” Keep those checks separate in your policy notes.
Use allow-lists and deny-lists with care. An IP rule may help protect an internal route, but it should not replace user identity checks. For public APIs, use keys or tokens tied to a customer, application, or account.
Rate limits should reflect the risk of each route. A search endpoint may allow more calls than a password reset endpoint. You can set limits by IP address, API key, user, or plan. Add quotas when you need a longer time window, such as a monthly partner allowance.
Then add resilience rules. A timeout stops a slow service from holding connections forever. A circuit breaker pauses calls to a failing service. Retries should be limited and safe, because repeating a payment or order request can cause harm.
Protocol translation is useful when clients use REST but an internal service uses gRPC. The gateway can also terminate TLS at the edge, then send traffic through a protected internal path. Response transformation can rename fields or combine results from several services into one client response.
Cache only responses that are safe to reuse. Public product data may be a good candidate. Personal account data usually needs stricter rules. Set clear cache keys and expiry times, then test what happens after a record changes.
Azure API Management supports routing, security, throttling, caching, and observability. Call-rate limiting is part of its traffic controls. Use the same checklist when comparing other gateways, even if their names for each policy differ.
By now, you should have a route file, an identity plan, limits for each important endpoint, and a failure response for every backend service.
Step 4: Add Observability, Governance, and Cost Controls
Api gateway services need a shared view of traffic, errors, latency, and usage cost.
Log enough detail to trace a request without storing sensitive payloads by default. A useful event may include a request ID, route, status code, duration, client type, gateway region, and service result. Redact tokens, passwords, health data, and private customer fields.
Build dashboards around questions people will ask during an incident:
- Which route has the highest error rate?
- Did latency rise after a release?
- Which customer or key is using the most calls?
- Are rejected requests caused by auth, quota, or backend failure?
Do not assume one gateway means one source of truth. A company may run Kong for one team and a cloud gateway for another. Separate gateways can split usage data and make customer analysis, audit work, and cross-team reporting harder. A unified analytics layer can normalize fields such as customer ID, API version, region, and plan.
Governance starts with a small rule set. Define naming standards for routes. Require an owner for every public API. Record the data classification, supported versions, retention policy, and emergency contact for each service. For a broader approach to enterprise API management, align these gateway policies with security, deployment, monitoring, and lifecycle processes across your organization.
Cost control also belongs in the gateway plan. Track calls by route and customer. Remove noisy health checks from billable paths when the platform allows it. Cache safe reads to reduce backend work. Set alerts before usage reaches a budget limit, especially for AI or large language model traffic.
Lakeway Web Development can help integrate these controls with the wider systems your business already uses. That gives managers a clearer view of how API traffic affects daily work, support tickets, and customer response time.
Choose one owner for the dashboard. If everyone owns observability, no one acts on the alert. The team should know who checks the signal, who fixes the service, and who tells customers what changed.
Step 5: Test, Version, and Scale Your Gateway Deployment
Finish your api gateway services setup with tests that cover behavior, failure, and growth.
Test the route map first. Send valid requests to each service, then send the wrong method, a missing field, an expired token, and an unknown path. Confirm that each rejection returns a safe status code and a useful message.
Test policy order as well. A request should not reach a backend before authentication and rate checks finish. Test a user with the right role, a user with the wrong role, and an unauthenticated caller.
Use contract tests for response shape. If a mobile app expects a field, removing that field can break the app even when the gateway remains healthy. OpenAPI documents can help teams agree on request and response formats. An API is an interface between software systems, and its specification describes how those systems communicate; API.
Version changes with care. A new route such as/v2/ordersis easy to understand, but it can create long-term support work. Keep old versions while active clients migrate. Publish a removal date and measure traffic by version before shutting anything down.
Test backward compatibility with real client patterns. A new optional field is usually easier to adopt than a renamed required field. If a response must change, consider a separate version or a translation policy at the gateway.
Scale the gateway across more than one instance. A single gateway can become a bottleneck or a single point of failure. Use health checks and route traffic only to healthy instances. For global users, consider regional placement so requests travel a shorter path. A managed gateway’s premium tier can support multi-region capacity distribution.
Self-hosted gateways need a clear upgrade plan. Pin versions, test configuration changes outside production, and keep a rollback image ready. Hybrid deployments need the same policy in each location, or users may receive different results based on where their request lands.
AI workloads add another concern. Token-aware limits can protect a budget when requests go to large language models. The policy should identify the user or application, cap usage, and return a clear response when the limit is reached.
Run a final load test that includes normal traffic, bursts, slow backends, and rejected requests. Watch gateway latency separately from backend latency. If the gateway adds too much work, simplify transformations or move heavy business logic into the service that owns it.
By now, you should have tested routes, documented versions, measured policy behavior, and written a scale plan with an owner.
FAQ
What is an API gateway?
An API gateway is a server that sits between clients and backend services. It gives clients one entry point while routing requests to the right service. Api gateway services may also check identity, enforce permissions, limit traffic, translate protocols, cache responses, and record operational data.
What are the main types of API gateway services?
The main types are managed cloud gateways, self-hosted gateways, and hybrid gateways. Managed options reduce platform work. Self-hosted options give your team more control over location and runtime settings. Hybrid designs connect cloud services with private or on-premises systems.
Are open-source API gateways free?
Some open-source API gateways can be used without a software license fee, but operations still cost time and infrastructure. You still need staff for upgrades, monitoring, security policies, backups, and incident response.
What should an API gateway handle?
An API gateway should handle shared edge tasks such as routing, request validation, authentication, authorization, rate limits, and logging. It can also support caching, protocol translation, response aggregation, and circuit breaking. Keep core business rules in backend services unless there is a clear reason to place them at the edge.
How do I scale an API gateway?
Scale an API gateway by running multiple healthy instances and spreading traffic across them. Add regional capacity when users are widely distributed. Test bursts and slow services before launch. Track gateway latency apart from backend latency so you can tell which layer needs more capacity.
Conclusion
Start with the gateway model your team can operate well, then prove the choice with route, security, cost, and failure tests. For a custom application that needs system integration and ongoing support, Lakeway Web Development can help you design an elegant gateway setup and connect it to scalable web or mobile software.